
Security-Minded Networking for Healthcare Organizations.
Segment clinical, administrative and guest networks, control who can reach what, and keep your perimeter running reliably.
Sound familiar?
Sensitive systems
Clinical and administrative systems need to be separated from everything else.
Many users and devices
Staff, guests and connected equipment share the same building.
Uptime matters
Network interruptions affect care and operations.
Practical tools for exactly this job.
Network segmentation
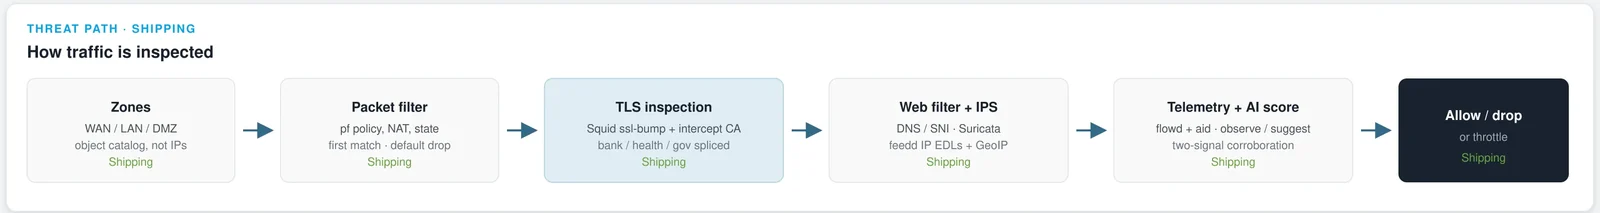
Zones keep clinical, admin, guest and device networks apart.
Access controls
Directory-backed authentication on Business+; admin roles and audit.
Health traffic not decrypted
If you use TLS inspection, health, banking and government sites are excluded.
Intrusion prevention
Suricata IPS and flood protection on every plan.
Operational reliability
Active/passive HA on Business+.
Reversible changes
Roll back any configuration change.
Protect sensitive environments.
Keep sensitive systems isolated while staff and guests stay connected.
- Zone-to-zone policy for clean segmentation
- Audit log and revision history with authors
- AI layer observes and suggests; a person approves
- Remote logging to your own syslog
About compliance. Rubix designs products with HIPAA safeguards in mind, such as access controls, encryption where applicable, and auditability. That doesn't make SecureGuard “HIPAA certified,” and it doesn't automatically make any deployment compliant — that depends on your configuration and processes. A Business Associate Agreement is available when applicable; contact sales@rubixtechnology.com.
Common questions
Is SecureGuard HIPAA compliant?
No software is compliant on its own, and SecureGuard isn't HIPAA certified. It provides controls — segmentation, access control, logging — that can support your compliance program.
Will TLS inspection decrypt patient portals?
TLS inspection is optional and zone-scoped, and it splices (does not decrypt) banking, health and government categories.
Can we keep logs off the firewall?
Yes. Remote syslog targets are configurable.
Protect the networks your care depends on.
Talk to us about your environment, or start with Community.