
Firewall Management Without the Headaches.
Write policy the way you think about your network, see exactly what a change will do, and undo it in one step if you need to.
From guesswork to confidence.
- Edit each service's settings separately
- Hope the pieces still agree
- Apply and find out
- Dig through backups to undo a mistake
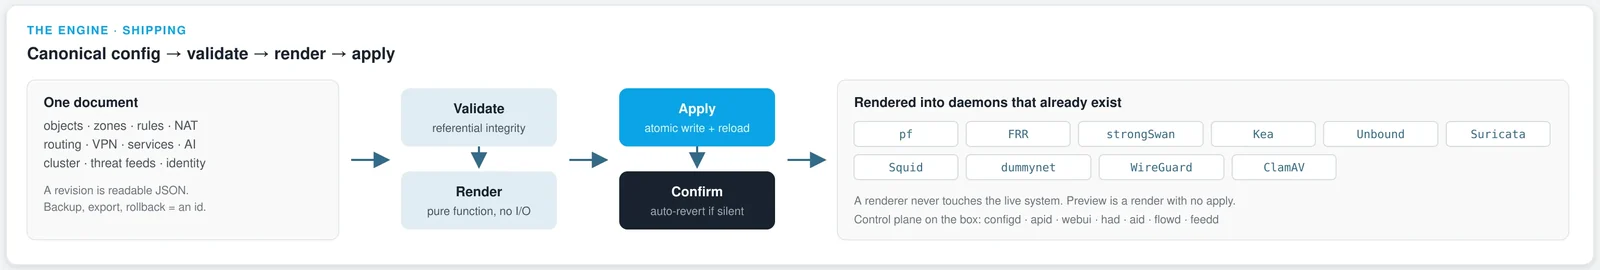
- Edit one validated configuration
- See what each change touches
- Commit, saved as a revision
- Roll back to any revision in one step
Policy that reads like your network.
Firewall policies
Rules are written zone-to-zone — LAN to WAN — and organized into titled, colored, collapsible groups with tags.
Rules and zones
Interfaces belong to zones. Move an interface between zones and no rule needs rewriting.
Network objects
Define hosts, networks, ranges, groups and services once and reuse them everywhere.
NAT kept separate
Masquerade, source NAT and port forwards get their own screens, never mixed into filter rules.
One-click disable
Turning a rule off — the most common troubleshooting step — is always one click.
Live logs per rule
Filter the live firewall log down to a single rule to answer “is this rule matching?” in seconds.
Make network changes with confidence.
Apply updates and back them out when needed.
- EditChange policy
- ValidateCatch mistakes
- ValidateChecked before it applies
- CommitApply atomically
- RevisionUndo any time
Select a step to see what happens.
Every state is a revision.
Each committed configuration is saved with its author and a parent pointer. That one design gives you history, backup, export and rollback.
- Backup is copying a revision
- Export is a readable JSON document
- Rollback is re-applying an earlier revision
- Upgrades can roll back too — separately — if a health check fails
Firewall management questions
Do I have to type IP addresses into rules?
No. Rules reference named objects — hosts, networks, ranges, groups and services — and zones. Rename or update an object and every rule using it follows.
Why is NAT on a separate screen?
Mixing NAT and filter rules is one of the most common sources of firewall confusion. SecureGuard keeps source NAT and port forwards on their own screens by design.
Is rollback available on the free plan?
Yes. Revisions and rollback are included on every tier, including Community.
Make your next firewall change a calm one.
Revisions and rollback are included free on Community.