
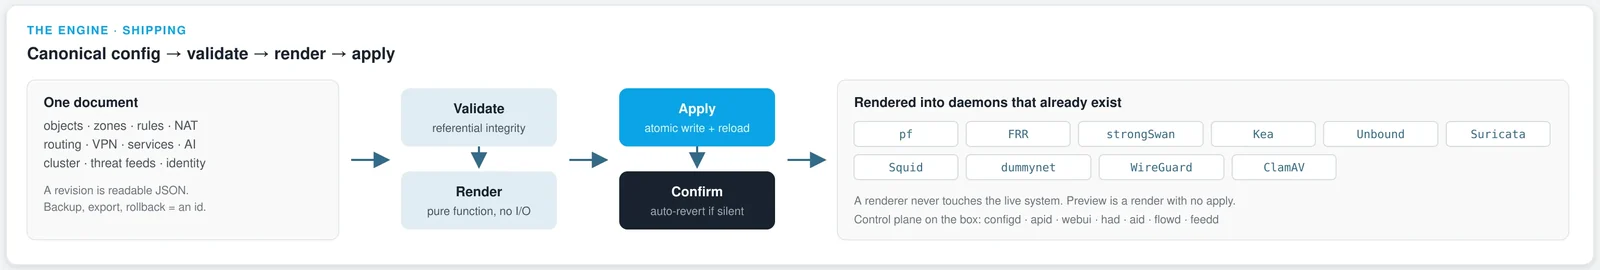
SecureGuard maintains one canonical, object-based, zone-aware configuration document and renders it into each daemon's native configuration on every change. Everything an operator sees or does is an operation on that one document.
Components and control-plane daemons
SecureGuard is a FreeBSD-based appliance image (ZFS on root) with pf as the packet filter. It doesn't reimplement routing, IKE, DHCP, DNS or intrusion detection — it orchestrates proven components (pf, FRR, strongSwan, Kea, Unbound, Suricata, Squid, WireGuard, dummynet) and owns one canonical, object-based, zone-aware configuration document that all of them are rendered from.
Control-plane daemons: configd (canonical document, validation, renderers, applier, revision store — single writer), apid (management API with admin auth, RBAC and audit), flowd (flow telemetry), aid (confidence scoring and graduated response), feedd (threat feeds) and had (HA state machine).
The commit pipeline
- EditChange policy
- ValidateCatch mistakes
- PreviewSee the diff
- CommitApply atomically
- RevisionUndo any time
Select a step to see what happens.
The console and any automation reach configd over a local socket. No component writes a daemon's configuration directly. Every change runs validate → render → apply, optionally followed by a confirm window. It's modeled on Junos and VyOS, and it's atomic.
In the web console (SecureGuard 1.1.225 or later), Save shows a review of the change (which parts of the configuration change and which services reload) before you click Apply. You can check Auto-revert so the change is undone unless you confirm it within 10 seconds to 1 hour; it is off by default and not available on the very first commit. Through the REST API the same steps are POST /api/v1/config/prepare, then confirm_timeout_sec on POST /api/v1/config/commit and POST /api/v1/config/confirm.
Validate
Validation is referential and returns every problem it finds, not just the first. A rule can't reference a zone or object that doesn't exist; a built-in zone can't be redefined; duplicate interface or zone names are rejected. A document that doesn't validate is never rendered and never applied.
Render & apply
Renderers are pure functions — a renderer never touches the live system, which is why a preview is just a render with no apply. The applier writes artifacts atomically and runs the reload actions; it supports a staging root and a dry run.
Confirm — the part that saves you
A commit may opt into a confirmed-commit window: configd applies the change and arms an auto-revert, and unless a matching confirm arrives inside the window it re-applies the previous revision. The revert runs under the same single-writer lock as any commit, so it can't race one. A plain commit with no window is permanent.
Revisions
Every config state is an immutable, content-addressed snapshot — the SHA-256 of its canonical JSON — with a parent pointer, an author and a message. From that one property: backup is copying a revision out; restore is loading and committing it; export needs no exporter; rollback is re-applying an earlier id; and HA config sync is shipping revisions between nodes.
Policy model
Policy is zone-to-zone and references named objects, never raw addresses. Renaming an object updates every rule that uses it; moving an interface between zones doesn't rewrite policy. See Policy.
The AI layer's place in this
The appliance runs a thin harness only — no model weights, no ML runtime. Suggestions are candidate config patches with a rationale and risk rating that go through the same validate → render → apply path. Autonomous enforcement, where enabled, is expressed as pf table entries with expiry, never as rules written into your ruleset. See AI security.
Something unclear? Tell us and we'll improve this page.